VPN vs Proxy: What’s the Difference and Which Do You Need?

Few questions in my field cause as much quiet confusion as VPN vs proxy, and one incident made that especially clear to me. A few years into my career, I got pulled into an incident review at a mid sized accounting firm. A staff member had been working from a hotel lobby, and she swore up and down that she was “protected” because she had a proxy extension running in her browser. To be fair, she was right that her IP address was hidden from the websites she visited. However, she was wrong about almost everything else. Her email client, her cloud sync app, and a background update service were all talking to the internet directly over the hotel’s open WiFi, completely untouched by that browser extension.
That conversation has stuck with me because it captures the whole VPN vs proxy confusion in one moment. People hear that both tools “hide your IP,” and as a result, they assume the two are interchangeable. They are not. In fact, they solve different problems, they sit at different layers of your system, and they ask you to trust different parties in different ways.
I have spent a good part of my working life configuring, auditing, and occasionally ripping out both of these technologies. So this article is my attempt to explain the difference the way I would explain it to a colleague over coffee, without the marketing gloss.
VPN vs Proxy: The Short Answer
If you only read one section, read this one.
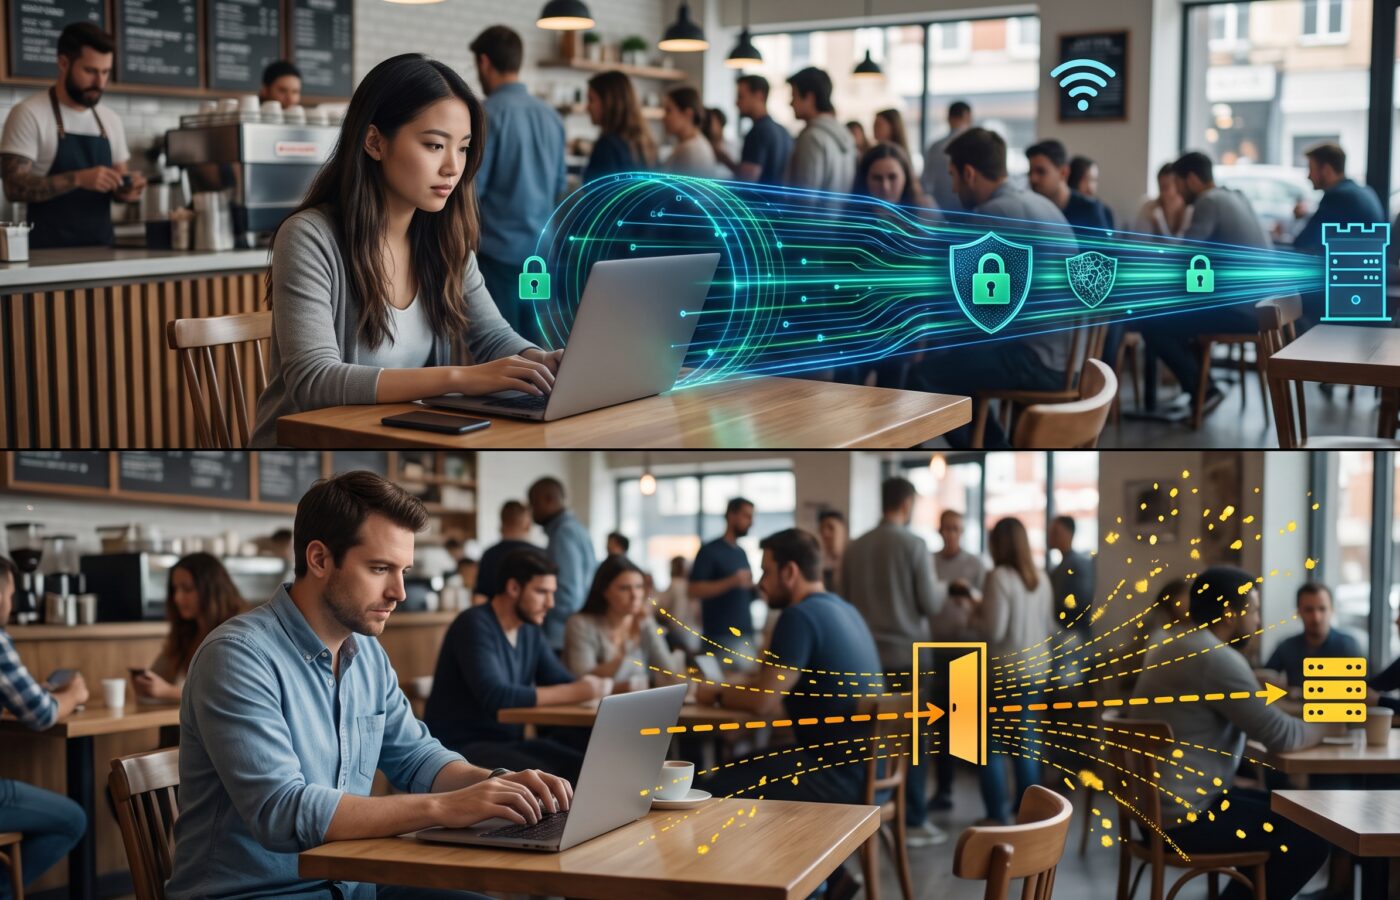
A proxy is a middleman for specific traffic. First, you point an application, usually a browser, at a proxy server. Then that server makes requests on your behalf, and the destination website sees the proxy’s IP address instead of yours. However, most proxies do not encrypt the connection between you and the proxy, and they only handle traffic from the apps you configure to use them.
A VPN, or virtual private network, on the other hand, creates an encrypted tunnel between your device and a VPN server. Once it is running, it typically captures all network traffic from your device at the operating system level, not just one browser tab. Consequently, anyone sitting between you and that server, such as the hotel WiFi owner, your internet provider, or someone sniffing packets on a coffee shop network, sees only scrambled data going to one destination.
In short, the core difference in the VPN vs proxy debate comes down to two words: scope and encryption. A proxy usually covers one app with no encryption of its own, whereas a VPN covers the whole device with encryption built in.
Everything else is detail. Important detail, though, so let’s get into it.
What a Proxy Does (and How It Differs From a VPN)
The word “proxy” gets thrown around loosely, and that is part of the problem. In networking, a proxy is any server that receives a request and forwards it somewhere else on someone’s behalf. Naturally, that definition covers a lot of ground.
Forward Proxies, Reverse Proxies, and the Ones You Meet Every Day
When consumers talk about proxies, they usually mean a forward proxy. For instance, Cloudflare’s learning center describes this kind of proxy as a server positioned in front of a group of client machines, relaying their requests out to the internet. In other words, your request goes to the proxy, the proxy fetches the page, and then the page comes back through the proxy to you.
There is also the reverse proxy, which flips the arrangement. A reverse proxy sits in front of web servers and makes sure visitors never talk to the origin server directly. For example, if you have ever visited a site protected by a CDN, you went through a reverse proxy without knowing it. Still, this kind matters to website owners rather than to someone protecting their own browsing, so I mention it mainly so you are not confused when you see the term.
Meanwhile, in corporate environments, forward proxies are everywhere. Companies use them to filter web content, cache frequently accessed files, log activity for compliance, and block known malicious domains. In those settings, therefore, the proxy is not there to give employees privacy. Instead, it is there to give the organization visibility and control. That alone should tell you something about what proxies are designed to do.
HTTP, HTTPS, and SOCKS5 Proxies Compared to a VPN Tunnel
Not all proxies speak the same language.
An HTTP proxy understands web traffic. It reads the requests your browser sends and passes them along. Because it understands the protocol, it can also modify headers, cache content, or block certain URLs.
An HTTPS proxy, in the consumer sense, handles encrypted web traffic. Here, however, is a subtle point that trips people up. When you visit a site over HTTPS through a proxy, the content between your browser and the website is still encrypted by TLS, which is the same encryption you would have without the proxy. In other words, the proxy did not add that encryption; the website did. Moreover, the proxy can still see which domain you are connecting to, and in some corporate setups that use TLS inspection, it can see much more.
A SOCKS5 proxy, by contrast, works at a lower level and does not care what kind of traffic it carries. As a result, it can handle web browsing, torrent clients, game traffic, and other protocols. Although it is more flexible than an HTTP proxy, by default it still does not encrypt anything, which is exactly where a VPN tunnel differs.
Finally, there are transparent proxies, which intercept your traffic without you configuring anything. Schools, libraries, and some ISPs use them for filtering, so you might never know one is there.
What a Proxy Does Well
I don’t want to undersell them, because proxies are genuinely useful. They are lightweight, quick to set up, and often cheaper than VPNs at scale. For example, if you are a developer testing how your site looks from different countries, a researcher collecting public data, or a business that needs to route specific application traffic through a fixed IP for allowlisting, a proxy can be exactly the right fit.
What a proxy does not do, in most cases, is protect you from someone watching your local network.
What a VPN Does That a Proxy Can’t
A VPN builds a tunnel. That is the most accurate single word I can give you.
When you connect to a VPN, your device first negotiates encryption keys with the VPN server. From that point on, packets leaving your device are wrapped in an encrypted layer before they hit the network. Therefore, the local network sees only that you are sending encrypted data to one IP address. Next, the VPN server unwraps the traffic and sends it out to the internet, and responses come back the same way.
NIST, the US National Institute of Standards and Technology, has published guidance on IPsec VPNs for two decades. Notably, their original guide lists the kinds of protection a VPN can provide: confidentiality, integrity, data origin authentication, replay protection, and access control. That list is worth reading slowly. After all, a proxy by default gives you none of those things, whereas a properly configured VPN gives you all of them, at least for the stretch between your device and the VPN endpoint.
The Protocols That Actually Matter
You will see a handful of protocol names in VPN apps. Here, then, is how I think about them in practical terms.
WireGuard is the modern favorite. Its codebase is small, which makes it easier to audit. In addition, it connects quickly and handles network changes, like moving from WiFi to mobile data, gracefully. Most reputable consumer VPNs now offer it.
OpenVPN has been the workhorse for years. It is mature, widely audited, and flexible enough to run on almost anything. Admittedly, it can be a bit slower than WireGuard, but it remains a safe choice.
IKEv2 with IPsec is standards based and common in enterprise and mobile settings. Because it reconnects well when your connection drops, phones handle it nicely. Furthermore, in 2020 NIST released a revised version of its IPsec VPN guide with updated cryptographic recommendations, so this protocol family continues to receive serious standards attention.
PPTP is old and broken. Consequently, if any app or router still offers it to you, treat that as a red flag about the whole product.
What a VPN Changes, and What It Doesn’t
Once your VPN is on, your ISP can no longer see which websites you visit, only that you are connected to a VPN. Similarly, public WiFi operators lose visibility into your traffic, and websites see the VPN server’s IP instead of yours.
But here is what I tell every client: the VPN provider now sees what your ISP used to see. In other words, you have not eliminated visibility; you have simply moved it. An EFF associate director told TIME a few years ago that VPNs tend to relocate privacy risk rather than remove it, which is the most honest one line summary of VPNs I have come across.
Likewise, a VPN does nothing about cookies, browser fingerprinting, logged in accounts, or malware already on your machine, which is why knowing how to spot a phishing email still matters with a VPN switched on. For example, if you log into your Google account over a VPN, Google still knows it is you.
VPN vs Proxy, Point by Point
Now let’s compare the two across the factors that actually matter in day to day use.
VPN vs Proxy Security and Privacy Differences
Encryption. A standard proxy does not encrypt traffic between your device and the proxy server. In contrast, a VPN encrypts everything between your device and the VPN server.
Coverage. A proxy usually works per application, so you configure your browser, or one tool, to use it. A VPN, however, runs at the operating system level and captures traffic from every app, including background services you forgot about.
Visibility to your ISP. With a proxy, your ISP can usually tell you are using a proxy and even which one. With a VPN, on the other hand, your ISP sees encrypted traffic going to the VPN server and little else.
Practical VPN vs Proxy Differences
Speed. Proxies can be slightly faster because there is no encryption overhead. That said, with modern protocols like WireGuard, the gap is often too small to notice on a decent connection.
Setup. Proxies are often just a settings field in a browser or an extension. VPNs, meanwhile, require a client app, although modern apps make it a one click affair.
Cost. Free proxies are everywhere, and paid proxies are common in business data workflows. By comparison, trustworthy consumer VPNs usually cost a few dollars a month.
Typical use. Proxies fit IP rotation, location testing, content filtering, and app specific routing. VPNs, by contrast, fit privacy on untrusted networks, remote access to company resources, and general traffic protection.
VPN vs Proxy Encryption: Where People Get It Wrong
I want to spend a moment here, because this is where most of the bad advice online lives.
What HTTPS Already Covers
Someone will say, “I don’t need a VPN, since almost every site uses HTTPS now.” They are partly right. HTTPS encrypts the content of your session with a website, so on open WiFi an attacker cannot read your banking password if the bank uses HTTPS properly.
However, what HTTPS does not hide is the metadata. Depending on configuration, the domain you are connecting to can still leak through DNS requests and other parts of the connection setup. Similarly, your DNS lookups may travel in plain text if they are not using an encrypted resolver. Besides, not every app on your phone uses HTTPS correctly. I have personally audited mobile apps that sent tokens over unencrypted connections or failed to validate certificates, and you cannot see that from the outside.
What a Proxy and a VPN Add on Top
A proxy does not fix any of that, because it typically only handles your browser and adds no encryption of its own. A VPN, on the other hand, fixes most of it for the local network, since every packet, including DNS when configured properly, goes through the tunnel.
On the opposite side, someone will say, “I use a VPN, so I’m anonymous.” That is not true either. Anonymity, after all, is a much higher bar. If you need real anonymity against a capable adversary, you are in Tor territory and operational security discipline, and even then it is hard. Ultimately, a VPN gives you privacy from your local network and ISP, but it does not give you invisibility.
The VPN vs Proxy Trust Problem Nobody Puts on the Sales Page
Every tool in this comparison asks you to trust someone. The real question, then, is who, and whether they deserve it.
Trusting a Proxy Operator
With a free public proxy, you are routing traffic through a server run by someone you know nothing about. As a result, they can log your requests. Moreover, if you visit any site without HTTPS, they can read and even modify what you see. I have seen free proxies inject ads and tracking scripts into pages. Hostinger’s comparison guide makes the same point I always make: whoever owns the remote server, proxy or VPN, can see your traffic, so choosing a trustworthy provider is not optional.
Trusting a VPN Provider
With a VPN, the trust question simply shifts to the provider. Do they keep logs? Have they been independently audited? Where are they legally based, and what can authorities compel them to hand over? Also, have they ever had a breach, and how did they handle it? For these reasons, I often send people to the EFF’s Surveillance Self Defense guide on choosing a VPN, because it walks through these questions without a product to sell.
Trusting Your Own VPN Gateway
There is also a security angle that home users rarely consider. For organizations, the VPN gateway itself is an attack surface. Specifically, in 2021 the NSA and CISA put out a joint information sheet warning that remote access VPN servers are entry points into protected networks and that multiple nation state groups had exploited known vulnerabilities in VPN devices. Accordingly, their recommendations included choosing standards based products, enforcing multifactor authentication, patching promptly, and disabling features that have nothing to do with the VPN itself. So anyone running a corporate VPN who has not read that document should.
Overall, the lesson is the same in both directions. Neither tool is safe by default. A well chosen, well configured VPN is a strong control, whereas a random free proxy is a liability wearing a privacy costume.
When a Proxy Beats a VPN
To be clear, proxies are not inferior; they are simply different. Here are situations where I would actually recommend a proxy over a VPN.
Web scraping and data collection. If you are gathering public pricing data or monitoring search results across regions, rotating residential or datacenter proxies are built for this. A VPN, by contrast, gives you one exit IP at a time and is the wrong shape for the job.
Location testing for websites and ads. Marketing teams and developers checking how a page renders in another country can use a proxy in the browser. That way, they avoid routing the rest of their machine through another region.
Corporate content filtering. Organizations that need to block categories of sites, log web activity for compliance, or cache content use forward proxies, often as part of a secure web gateway.
Application specific routing. Sometimes one tool needs to come from a fixed IP that a partner has allowlisted, while everything else on the machine uses the normal connection. In that case, a proxy configured just for that tool keeps things clean.
Low risk tasks where speed matters more than privacy. If you simply want to see a region specific page and you are on a network you trust, then a reputable proxy is fine.
In each case, the common thread is that the proxy is solving a routing or identity problem, not a confidentiality problem.
When a VPN Beats a Proxy
Public and untrusted networks. Airports, hotels, cafes, and conference WiFi are the textbook case. Here, every app on your device benefits, not just the browser.
Remote work. Employees accessing internal systems from home or on the road need an encrypted, authenticated path into the company network, which is exactly what corporate VPNs were built for. (If you work remotely, see our tips on staying productive working from home.) That said, many organizations are now layering in or migrating toward zero trust network access, which checks identity and device health for each application rather than granting broad network access.
Hiding browsing from your ISP. In many countries, ISPs can collect and sometimes monetize browsing data. A trustworthy VPN, therefore, moves that visibility away from the ISP.
Travel to regions with heavy network monitoring. A VPN can help protect communications. Even so, you should understand local laws before using one, since some countries restrict VPN use.
Protecting devices with lots of background traffic. Phones are the best example, because dozens of apps phone home all day. A VPN catches all of them, while a browser proxy catches none of them.
VPN vs Proxy for Businesses
If you run IT for a company, the question is rarely an either/or. In practice, most mature environments use both, plus other controls.
A typical setup I would sign off on looks like this. First, remote employees connect through a standards based VPN or a zero trust access broker with multifactor authentication. Second, outbound web traffic, whether from the office or tunneled back from remote devices, passes through a secure web gateway that acts as a filtering proxy. Third, public facing applications sit behind a reverse proxy or CDN that absorbs attacks and hides origin servers. Finally, DNS is filtered and logged.
Each layer covers a gap the others leave open. The VPN protects the transport, the forward proxy enforces policy on what users can reach, and the reverse proxy protects what you publish. So when someone asks me which one their business needs, the honest answer is usually “both, for different reasons.”
Common VPN and Proxy Mistakes I See
A few patterns come up so often in audits that they are worth naming.
Trusting a browser extension to protect the whole device. This was the accounting firm story. Extensions labeled “VPN” are frequently just proxies for the browser, so read the description carefully.
Using free VPNs on work devices. Free VPN apps have to make money somehow, and logging and selling data is one common way. On a work laptop, consequently, that is a data protection incident waiting to happen.
Ignoring DNS and IPv6 leaks. Some VPN configurations route IPv4 traffic through the tunnel while IPv6 or DNS requests slip out the normal route. Good clients handle this; nevertheless, test yours with a leak checking site after setup.
Running without a kill switch. If the VPN connection drops, a device without a kill switch will quietly fall back to the open network. Therefore, anyone who genuinely needs the protection should turn the kill switch on.
Leaving the corporate VPN appliance unpatched. The NSA and CISA guidance exists precisely because attackers love VPN gateways. In other words, a forgotten patch on an edge device can undo every other control you have.
VPN vs Proxy: Which Do You Need?
Ask yourself one question: are you trying to change where your traffic appears to come from, or are you trying to stop people from seeing your traffic?
If it is the first, and only for a specific app or task, then a reputable proxy is probably enough and may even be the better tool.
Should it be the second, or if you are on any network you don’t control, then you need a VPN from a provider you have actually vetted.
And if you are responsible for an organization, you likely need both, configured deliberately, patched regularly, and reviewed by someone who understands what each one does and does not cover.
Ultimately, the worst outcome is not choosing the “wrong” tool. Rather, it is believing you are protected when you are not. That hotel lobby incident was not caused by a bad proxy; instead, it was caused by a reasonable person misunderstanding what the proxy was doing. Now, however, you know the difference.
Frequently Asked Questions
Is a VPN more secure than a proxy?
For most users, yes. A VPN encrypts traffic between your device and the VPN server and covers every app on the device, whereas a standard proxy usually encrypts nothing and covers only the apps you configure. NordVPN’s comparison guide summarizes this scope difference clearly.
Can I use a VPN and a proxy at the same time?
Yes. For example, a business may have remote devices connect over a VPN and then pass web traffic through a filtering proxy. For individuals, however, combining them rarely adds much and can slow things down. Cloudflare’s forward and reverse proxy explainer helps clarify where each proxy type sits in the chain.
Does a proxy hide my IP address?
It hides your IP from the destination website, which sees the proxy’s address instead. Nevertheless, your ISP and anyone on your local network can still see that you are connecting to the proxy. Hostinger’s tutorial covers what each party can observe.
Are free VPNs or free proxies safe to use?
Treat them with real caution. Whoever runs the server can see your traffic, and free services often fund themselves through logging, ads, or data sales. The EFF’s guide to choosing the VPN that’s right for you explains what to check before trusting any provider.
Will a VPN make me completely anonymous online?
No. A VPN shifts visibility from your ISP to your VPN provider, and furthermore, it does nothing about cookies, logged in accounts, or browser fingerprinting. TIME’s reporting on VPN privacy includes an EFF expert’s explanation of why VPNs relocate risk rather than eliminate it.
What VPN protocol should I choose?
WireGuard, OpenVPN, and IKEv2/IPsec are all solid choices from reputable providers. By contrast, avoid PPTP. For the standards view of IPsec, see NIST’s Guide to IPsec VPNs.
Do businesses still need VPNs with zero trust tools available?
Many still use VPNs, often alongside zero trust access tools. Either way, what matters most is hardening whatever you deploy. The NSA and CISA guidance on remote access VPNs lays out selection and hardening steps for organizations.
References
- National Institute of Standards and Technology. Guide to IPsec VPNs: Recommendations of the National Institute of Standards and Technology
- National Institute of Standards and Technology. NIST Revises Guide to IPsec VPNs (Revision 1)
- Cybersecurity and Infrastructure Security Agency. CISA and NSA Release Guidance on Selecting and Hardening VPNs
- National Security Agency. NSA, CISA Release Guidance on Selecting and Hardening Remote Access VPNs
- Cloudflare Learning Center. What Is a Reverse Proxy? Proxy Servers Explained
- Electronic Frontier Foundation, Surveillance Self Defense. Choosing the VPN That’s Right for You
- TIME. Should You Use a VPN for Internet Privacy?
- NordVPN. Proxy vs. VPN: What Are the Main Differences?
- Hostinger. Proxy vs VPN: What’s the Difference?
- SecurityWeek. NSA, CISA Issue Guidance on Selecting and Securing VPNs